
Advisory CISO
A CISO’s judgment, on your side of the table.
We advise boards on what to oversee, investors on what to back, founders on how to win the CISO, and corporations on security strategy and how to build the program.
Who we work with
Four seats at the table. Four different questions about the same risk.
Our job is to answer each one in the terms that seat uses.
Boards
“Are we overseeing this well, and how would we know?”
- Cyber and AI risk oversight
- Committee charters and audit or risk integration
- Director briefings built around what the board oversees
Venture Investors
“Will a CISO actually buy this, and where is our portfolio exposed?”
- Security startup thesis, from the buyer’s side
- Portfolio risk reviews
Founders
“Why does the CISO like the demo and still not buy?”
- Go-to-market with CISO buyers
- Messaging in the terms CISOs budget against
- Sales enablement that earns a CISO’s trust
Corporations
“What should our security strategy be, and how do we build the program to deliver it?”
- Security strategy and program roadmaps
- Program, policy and governance build-out
- Board and executive committee reporting
How we work
Senior judgment, applied to the decision in front of you.
Scoped to the moment
Every engagement starts from what is forcing the timing: a board meeting, a deal, an audit, a hire you have not made. Scope, timeline and budget follow from that.
Senior-led
Every engagement is led personally by our principal, Antonio Bovoso, from the first conversation to the final deliverable.
A straight answer on fit
If the work is not ours to do, you will hear that in the first conversation, along with who we would call instead.
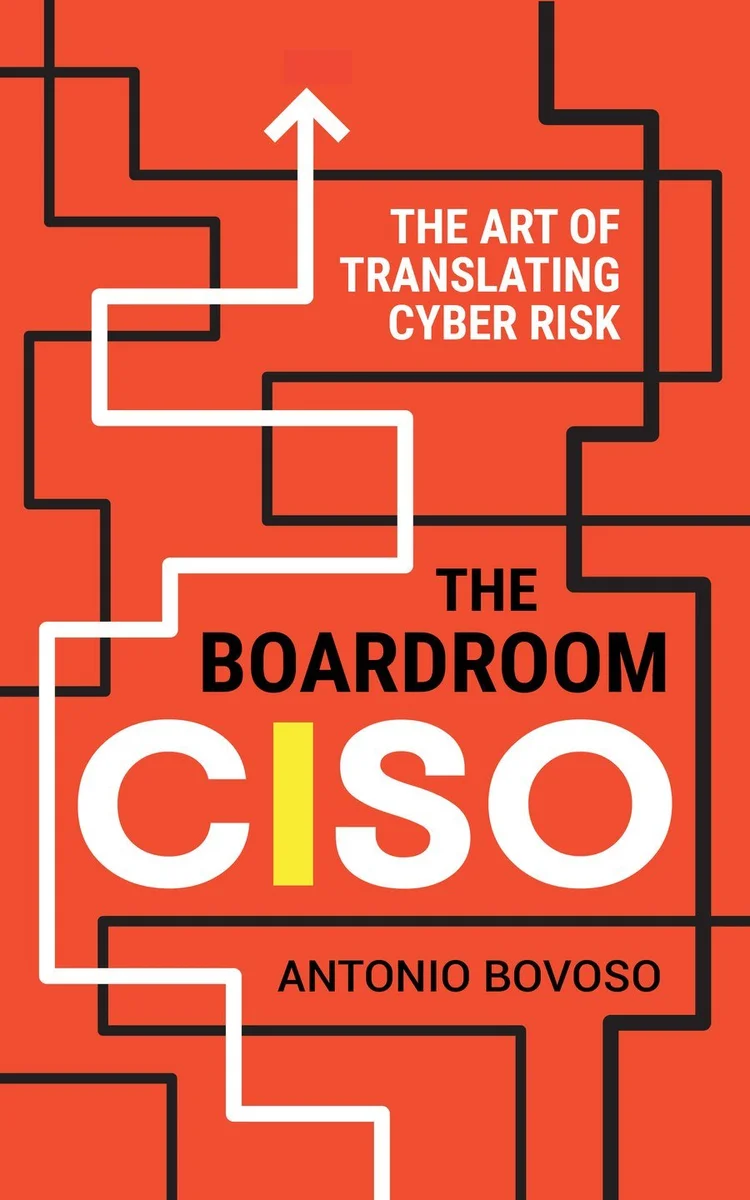
Consiro Press · Now available
The Boardroom CISO
The Art of Translating Cyber Risk
Boards want to understand cyber risk. CISOs want to be understood. The same conversation fails in the same ways in boardrooms across every industry. This is a practitioner’s guide to closing that gap.
Hardcover · Paperback · Kindle
Our principal
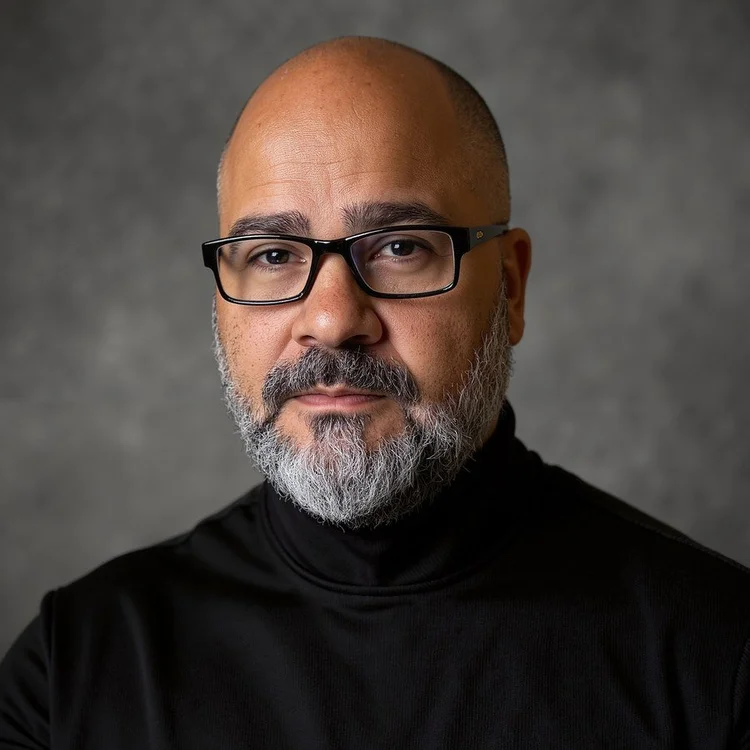
Antonio Bovoso
He has spent more than 25 years in cybersecurity, at Deloitte, IBM, HP and Bank of America, and as CISO of Sage Therapeutics.
He sits on five advisory boards for cybersecurity, AI and compliance companies and reviews for the Cybersecurity Canon. He wrote The Boardroom CISO about the failure he saw most often in the role: cyber risk lost in translation between the security team and the board.
Start a conversation
Bring us the decision in front of you.
Tell us what is forcing the timing and where you stand today. We will tell you how we can help.